Malware cleanup, security hardening and WooCommerce performance work for a US RV brand — sales increased by 40%.

A US RV brand running two compromised WordPress/WooCommerce sites — we cleaned up the breach, rebuilt the security architecture, and turned our attention to performance and conversion. Now their long-term development and security partner.
Motorhometires.com and shinyrv.com had been actively compromised, injecting malicious code and redirecting visitors to malware-serving domains.
Attackers had established persistent access through compromised credentials and hidden backdoor files — making a simple plugin-scan insufficient.
Both sites had zero WAF protection, leaving them fully exposed to automated scanning, brute-force, and injection attacks around the clock.
Both properties — motorhometires.com and shinyrv.com — belong to the same US-based client in the RV industry, and both had been compromised. The priority was clear: contain the damage, understand how the attackers got in, and make sure it could not happen again.
Page load times of 5–8 seconds were driving high bounce rates and directly suppressing WooCommerce checkout completion on both properties.
The checkout flows had accumulated years of technical debt, causing measurable cart abandonment with no optimisation ever having been performed.
Motorhome Tires required tiered discount logic by tyre brand with dynamic sale banners — functionality unavailable in any off-the-shelf plugin.
We began with a full malware cleanup and forensic investigation, locked down both sites with Cloudflare WAF rules, Redis caching and a complete security architecture rebuild.
Performance was our next priority — page speed overhauls, WooCommerce optimization and a custom discount plugin with tiered pricing logic to increase conversions.
We continue as their trusted development and maintenance partner, supporting ongoing improvements, marketing initiatives and new feature development.
With the security incident fully resolved and the sites hardened against future attacks, the performance and conversion work started paying off immediately — checkout got faster, discount logic got smarter, and sales increased by 40%.
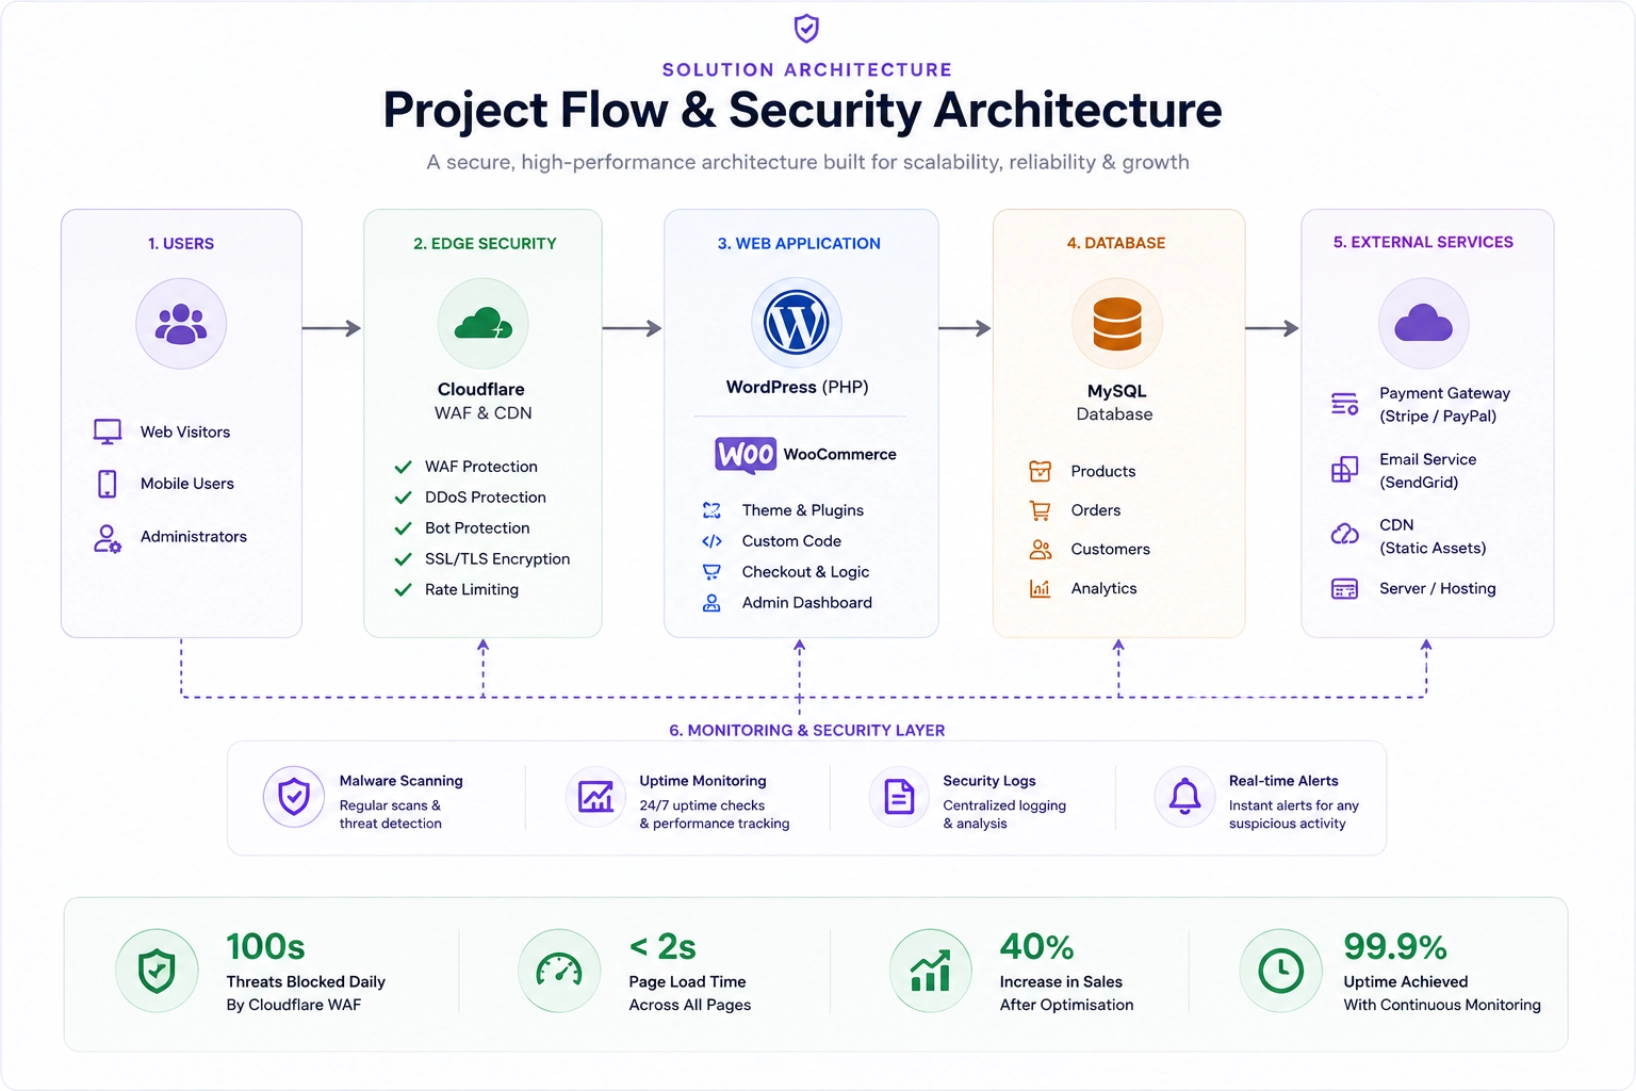
Every tool was selected for security, performance, and long-term maintainability — from the WAF layer down to the WooCommerce checkout.
We modernised fragmented workflows and manual tasks into an intelligent system that improves efficiency and client experience.
Both sites infected with malware redirecting visitors to malicious domains
Clean, secure sites with zero infections and continuous threat monitoring in place
No Web Application Firewall — sites fully exposed to automated attacks
Hardened Cloudflare WAF with custom ruleset blocking hundreds of daily threats
Page load times of 5–8 seconds reducing conversions across both properties
Sub-2 second load times with Redis caching and full CDN coverage on all pages
WooCommerce checkout causing significant cart abandonment
Optimised checkout flow delivering a 40% uplift in completed sales
No brand-based discount or promotional pricing capability
Custom tiered pricing plugin with dynamic sale banners and brand-level logic
No ongoing monitoring — breaches discovered only after significant damage
Proactive monitoring, alerts, and a dedicated long-term development partner
The recovery began with forensic investigation to trace every entry point. Once the threat was contained, attention shifted to performance and conversion — turning a security incident into a platform for sustained growth.
As adoption stabilised, we extended the engagement into ongoing development and introduced the custom pricing plugin to drive repeat business.
Both sites fully recovered with zero security incidents since remediation
40% increase in e-commerce sales across both properties
Sub-2 second load times achieved across all key pages
Custom discount plugin drives repeat purchases with tiered brand pricing
Cloudflare WAF actively blocking hundreds of daily attack attempts
Ongoing development partnership delivering continuous improvements
Both sites have maintained a clean security record since remediation. Combined with performance improvements and the custom discount plugin, the partnership has delivered measurable, sustained revenue growth.

The Restaurant Zone — full-stack development and platform integration for a national US hospitality recruiter. →

Outlier Limited — multi-platform app and web development. →

OMEX Industries — headless platform for a US industrial manufacturer with 50,000+ products. →
Tell us about your project — we'll reply with a clear plan and a fixed quote, usually within one business day.